AI GOVERNANCE · LEGAL INSIGHTS
Understanding EU AI Act obligations
A practical overview of prohibited practices, high-risk systems, transparency duties and general-purpose AI models.
The EU AI Act establishes a risk-based regulatory framework for AI systems within its scope. The obligations that apply depend on the system’s intended purpose, the risks it presents and the role an organisation plays in the AI value chain.
The framework is commonly illustrated through four risk tiers, with the respective compliance requirements:
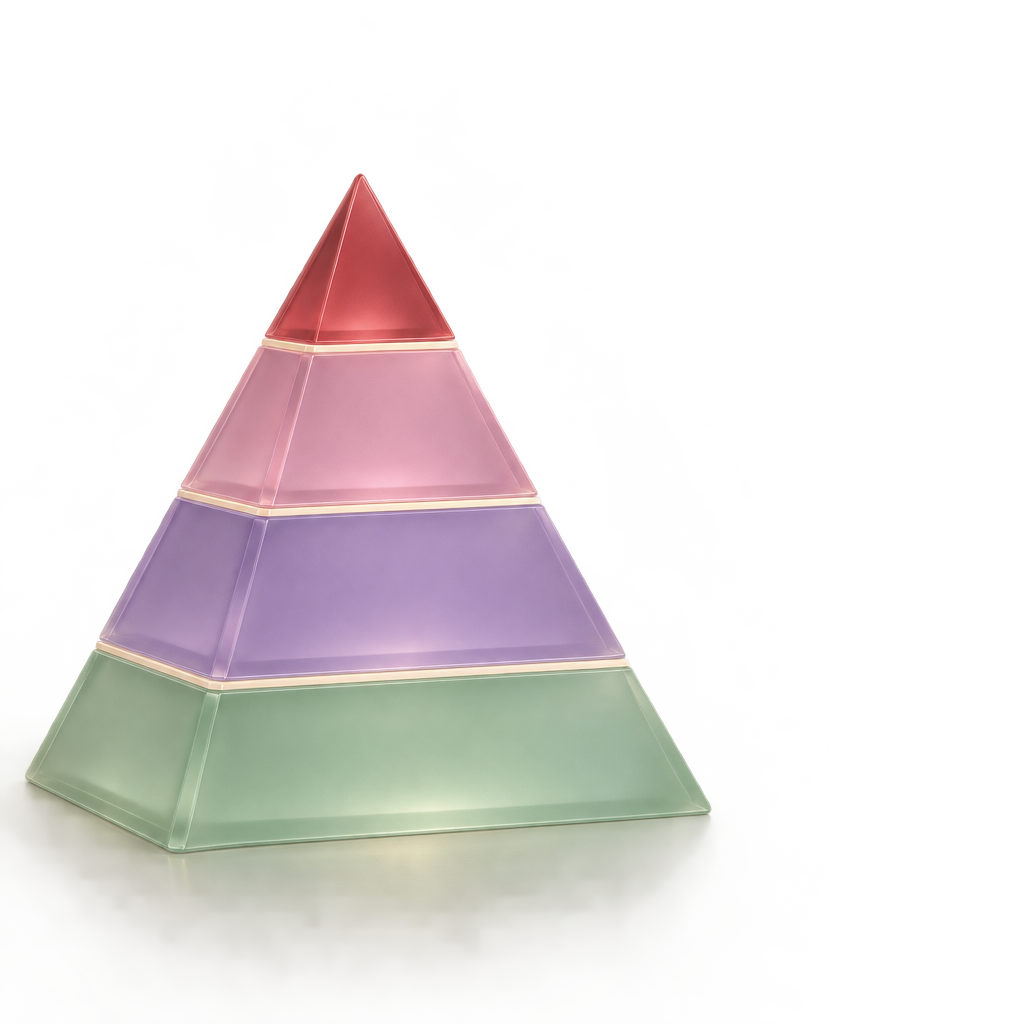
- UNACCEPTABLE RISKProhibited practices
- HIGH RISKCompliance requirements
- TRANSPARENCY RISKSDisclosure and marking obligations
- MINIMAL RISKNo risk-specific requirements
- Unacceptable risk: AI practices that are prohibited under Article 5 because they threaten life, safety or fundamental rights, subject to the conditions and exceptions set out in that Article.
- High risk: systems that meet the classification criteria in Article 6 and the relevant Annexes, including certain systems used in sensitive sectors or as critical safety components.
- Limited risk: certain systems and uses that are subject to specific transparency obligations, including informing people that they are interacting with AI or that content has been artificially generated or manipulated.
- Minimal risk: systems without additional risk-category-specific requirements. Other applicable obligations remain unaffected.
The framework at a glance
- Providers of high-risk AI systems and providers of general-purpose AI (GPAI) models carry substantial compliance responsibilities.
- Deployers using AI under their authority within the EU, or third-country providers and deployers whose AI outputs are intended to be used within the EU, also have obligations.
- The EU AI Act mandates transparency, risk management and governance standards, backed by oversight from national competent authorities and the Commission’s AI Office, according to their respective responsibilities.
Key application dates
- 1 August 2024: the AI Act entered into force.
- 2 February 2025: the original Article 5 prohibitions and the AI literacy provisions began to apply.
- 2 August 2025: the GPAI framework began to apply, subject to transitional arrangements, including for models already on the market.
- 2 August 2026: Article 50 transparency obligations began to apply.
- 2 December 2026: the new prohibitions concerning non-consensual intimate material and child sexual abuse material apply. The targeted Article 50(2) transition for qualifying pre-existing generative AI systems also ends.
- 2 December 2027: Chapter III, Sections 1–3, apply to high-risk systems under Article 6(2) and Annex III, subject to the Regulation’s transitional provisions.
- 2 August 2028: Chapter III, Sections 1–3, apply to high-risk systems under Article 6(1) and Annex I, subject to the Regulation’s transitional provisions.
The later high-risk dates reflect Regulation (EU) 2026/1744, the Digital Omnibus on AI. They do not postpone the entire AI Act or remove obligations that already apply.
I. Unacceptable risk: prohibited AI practices
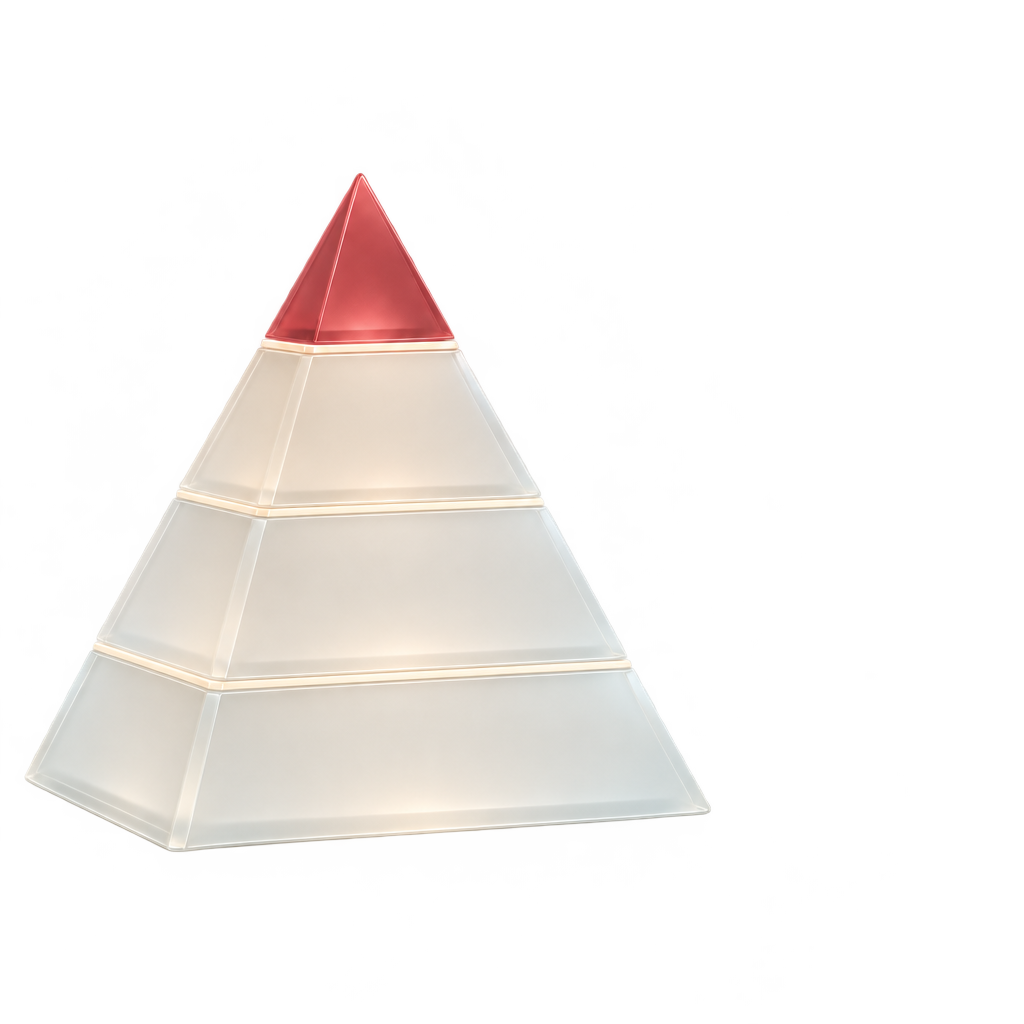
Article 5 explicitly prohibits specified practices that infringe upon fundamental rights or involve harmful manipulation. Subject to the conditions and exceptions in that Article, the prohibited categories include:
- harmful AI-based manipulation and deception
- harmful AI-based exploitation of vulnerabilities
- social scoring leading to the prohibited forms of detrimental or unfavourable treatment
- individual criminal offence risk assessment or prediction based solely on profiling or personality traits and characteristics
- untargeted scraping of facial images from the internet or CCTV material to create or expand facial recognition databases
- emotion recognition in workplaces and educational institutions, except where intended for medical or safety reasons
- biometric categorisation to deduce or infer specified sensitive characteristics, subject to the statutory exclusions
- real-time remote biometric identification for law enforcement purposes in publicly accessible spaces, subject to narrowly defined exceptions
- specified practices involving AI systems that generate or manipulate non-consensual intimate material or child sexual abuse material (CSAM), including certain AI “nudification” applications
The original prohibitions have applied since 2 February 2025. Additional prohibitions concerning AI systems generating or manipulating non-consensual intimate material and child sexual abuse material apply from 2 December 2026. Their precise scope, including the distinction between provider and deployer conduct and the applicable safeguards, must be assessed under the amended Article 5.
II. High risk: classification and compliance
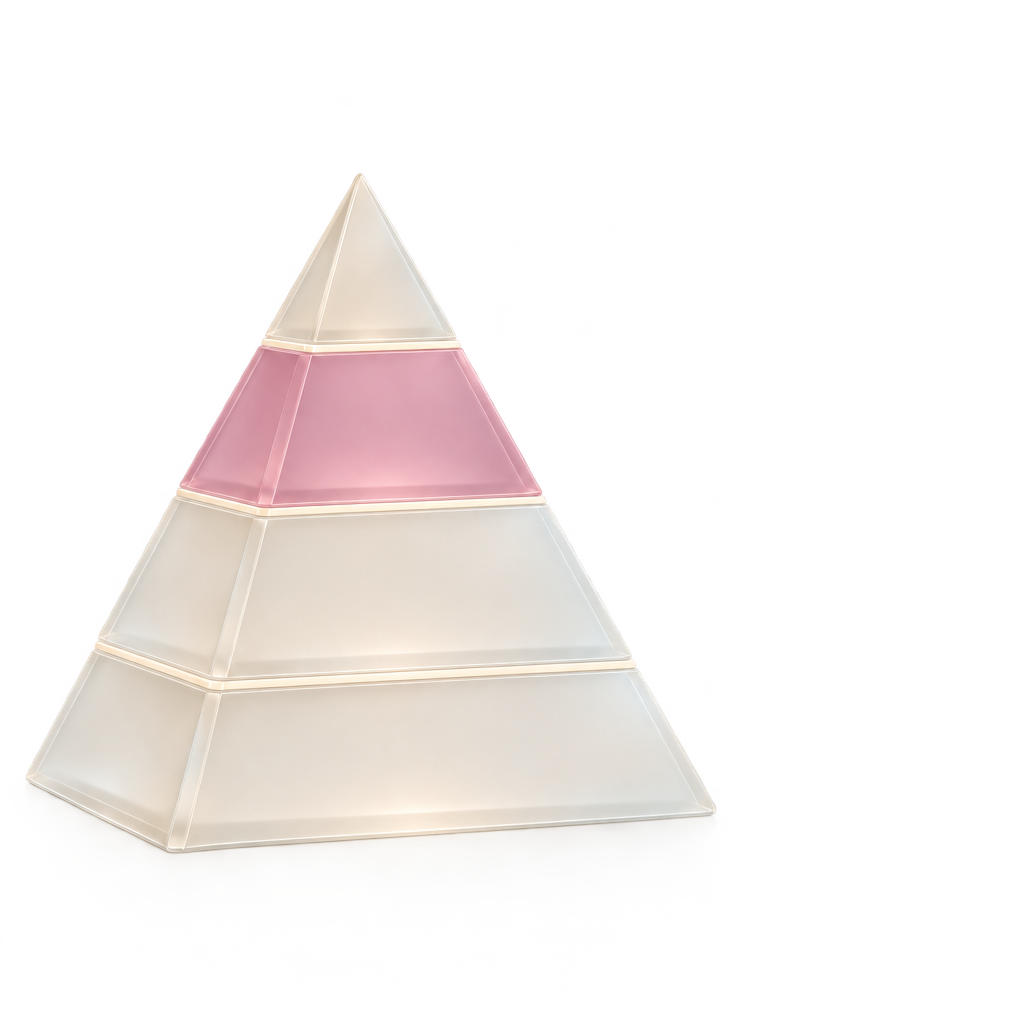
High-risk classification follows two main routes: certain products or safety components covered by Annex I, where the Article 6(1) conditions are met; and the specific use cases listed in Annex III under Article 6(2).
Not every tool used in a sensitive sector is automatically high risk. It is important to examine such tools on a case-by-case basis in terms of their intended purpose, the exact Annex entry and any applicable Article 6(3) exception.
An AI system referred to in Annex III that performs profiling of natural persons is always considered high risk.
Subject to the relevant classification criteria, high-risk systems include:
- AI safety components in critical infrastructure (e.g. transport), the failure of which could put citizens’ lives and health at risk
- AI solutions used in educational institutions that may determine access to education or the course of someone’s professional life (e.g. scoring of exams)
- AI-based safety components of products (e.g. an AI application in robot-assisted surgery)
- AI tools for employment, management of workers and access to self-employment (e.g. CV-sorting software for recruitment)
- certain AI use cases concerning access to essential private and public services (e.g. assessing creditworthiness when determining access to a loan)
- certain AI systems used for remote biometric identification, emotion recognition and biometric categorisation, where not prohibited
- AI use cases in law enforcement that may interfere with people’s fundamental rights (e.g. evaluation of the reliability of evidence)
- AI use cases in migration, asylum and border control management (e.g. automated examination of visa applications)
- AI solutions used in the administration of justice and democratic processes (e.g. certain AI solutions assisting in the preparation of court rulings)
Obligations for providers of high-risk AI systems
The prescribed requirements and obligations include those in Articles 8–21, together with the relevant conformity assessment, marking, registration and post-market provisions. Providers must comply with the applicable requirements before placing a high-risk AI system on the market or putting it into service, and meet their ongoing obligations:
- risk management system (establish, implement and maintain a risk management system across the AI lifecycle)
- data governance (where applicable, training, validation and testing datasets must meet the relevant requirements for relevance, representativeness, completeness and freedom from errors to the best extent possible)
- technical documentation (necessary to demonstrate compliance for regulatory review)
- record-keeping (automatic event-logging features to identify health, safety or fundamental rights risks, facilitate post-market monitoring and track substantial modifications)
- instructions for use (provided to downstream deployers)
- human oversight (measures enabling meaningful oversight)
- accuracy, robustness and cybersecurity (appropriate performance levels and resilience against errors and cyber threats)
- quality management system (supporting ongoing legal compliance)
- conformity assessment and CE marking (including an EU declaration of conformity, with corrective action where required)
- registration where required in the EU database, and compliance with applicable accessibility requirements
Obligations for deployers of high-risk AI systems (Article 26)
- use in accordance with instructions
- assignment of human oversight
- monitoring and retention of logs under their control where required
Certain deployers must also carry out a fundamental-rights impact assessment under Article 27. Data-protection obligations, including a DPIA where required, remain separate and may apply alongside the AI Act.
III. Limited risk: specific transparency obligations (Article 50)
Article 50 sets forth different obligations according to the AI system and the activity concerned. Providers of systems intended to interact directly with people must ensure that people are informed that they are interacting with AI, unless this is obvious in the circumstances.
Providers of systems generating synthetic audio, images, video or text must ensure that outputs are marked in a machine-readable format and detectable as artificially generated or manipulated, subject to the statutory qualifications.
In addition, deployers using AI systems to generate or manipulate text published to inform the public on matters of public interest must disclose that the published text has been artificially generated or manipulated. This disclosure obligation does not apply where the content has undergone human review or editorial control and a natural or legal person holds editorial responsibility for its publication. It also does not apply where such use is authorised by law to detect, prevent, investigate or prosecute criminal offences.
The human-review exception concerns this specific text-disclosure obligation, not all transparency duties under Article 50.
Typical applications include chatbots and deepfakes.
These obligations have applied since 2 August 2026. A targeted transition until 2 December 2026 concerns Article 50(2) marking for providers of qualifying generative AI systems placed on the market before 2 August 2026. It is not a general grace period for all Article 50 duties.
IV. Minimal / no risk
No category-specific requirements are introduced for minimal- or no-risk AI systems, such as AI-enabled video games or spam filters.
However, providers and deployers of minimal- or no-risk AI systems remain subject to the Article 4 obligation concerning the adoption of measures to support the development of AI literacy of their staff and other persons dealing with the operation and use of AI systems on their behalf.
Minimal-risk status does not itself create an exemption from that obligation. Data protection, intellectual property and other applicable laws continue to apply.
General-purpose AI models – GPAI: a separate layer
GPAI models (Chapter V, Articles 51–56) can perform a wide range of tasks and may be integrated into many downstream applications, serving as foundational building blocks for a wide range of AI systems.
Under Article 53, GPAI model providers must draw up and maintain technical documentation and provide specified information to downstream system providers that integrate the model into their own AI systems, subject to the limited exemptions for qualifying free and open-source models. They must also put in place a policy to comply with EU copyright law and publish a sufficiently detailed summary of the content used to train the model, in line with the AI Office template.
Models with systemic risk
For GPAI models classified as presenting systemic risk, Article 55 additionally requires providers to carry out model evaluation and adversarial testing, assess and mitigate systemic risks at Union level, track and report serious incidents to the AI Office, and ensure adequate cybersecurity protection for the model and its physical infrastructure.
A GPAI model with systemic risk can serve as the foundation for, or be integrated into, a downstream high-risk AI system. In that case, the GPAI model remains subject to the applicable Chapter V rules, while the resulting AI system is assessed under the relevant system-level provisions. Therefore, a GPAI model and a downstream AI system should not be treated as interchangeable legal categories.
Where organisations should start
- Identify the AI systems and models developed, supplied or used by the organisation.
- Determine the organisation’s legal role for each activity: provider, deployer, importer, distributor or another relevant operator.
- Check prohibited practices first, then assess high-risk classification, transparency duties and any GPAI obligations.
- Map the applicable dates, transitional provisions, evidence and responsible people for each obligation.
The practical question is not simply “Which tier does this tool belong to?” It is “Which obligations apply to this system, this use and this organisation?”